
Deep Blue Krypto · partner fact sheet
QryptoTrust
Post-quantum data trust and identity for enterprise, including the ML-DSA identity-cube visualization and a multi-format certificate analyzer.
- Principal
- Jason Hilker, Co-Founder and CEO
- Domain
- Post-quantum data trust and identity
- Written for
- Defense PQC and collision-avoidance buyers
- Signature base
- ML-DSA (FIPS 204) identity and certificate analysis
What QryptoTrust does
Trust you can read, on data in motion and at rest.
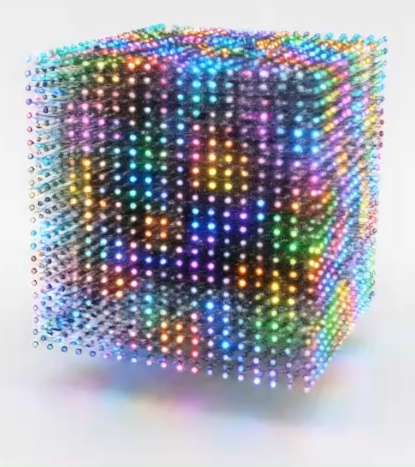
QryptoTrust gives enterprises post-quantum data trust and identity: a way to prove who signed a record, that it was not altered, and that the identity behind it is post-quantum sound. Two parts make the abstract concrete. The ML-DSA identity cube renders a lattice signature as a structure an operator can inspect rather than take on faith, and the multi-format certificate analyzer reads a certificate across common encodings and reports what it actually asserts. The result is trust that a reviewer can see, not a claim buried in a protocol.
Why it matters to Deep Blue Krypto clients
Defense data crosses enterprise ground, and trust has to survive the crossing.
Deep Blue Krypto clients rarely live in a closed loop. Sensor data, mission records, and the certificates that bind devices and suppliers move across enterprise and commercial systems before they reach a defense decision. That crossing is where identity gets lost and where a stale or malformed certificate slips through. QryptoTrust addresses the crossing directly: it analyzes the certificates a program depends on across formats, and it makes a post-quantum identity legible to the person who has to sign off on it. For a collision-avoidance program, the payoff is upstream confidence that the records feeding the decision carry a verifiable, post-quantum identity rather than an assumed one.
Core capabilities
What the data-trust layer provides.
- Post-quantum identity. ML-DSA (FIPS 204) signatures that bind a record to a verifiable identity.
- Certificate analysis. A multi-format analyzer that reads a certificate across common encodings and reports what it asserts.
- Legible trust. The identity-cube view turns a lattice signature into a structure an operator can inspect.
- Enterprise fit. Built for commercial and enterprise data-sovereignty buyers, so it travels with data that leaves a closed network.
- Honest reporting. The analyzer states what a certificate contains, without inventing assurances it cannot read.
Where it meets Deep Blue Krypto
The record of trust behind the mission record.
Deep Blue Krypto owns the contested-edge and collision-avoidance problem; QryptoTrust owns the identity and certificate layer that the records in that problem depend on. When an engagement needs to prove that a data product is what it claims to be, across the enterprise systems it passed through, the two capabilities fit together without a seam.
Learn more about QryptoTrust.
Review QryptoTrust directly, or tell Deep Blue Krypto where in your data chain trust is being assumed rather than proven.
Provenance: QryptoTrust description and principal title (Jason Hilker, Co-Founder and CEO) are FACT from the Deep Blue Krypto partner dataset; the ML-DSA standard reference is FACT; the defense and collision-avoidance fit framing is INFERENCE and the host client sector is inferred, confirm. No security claim here is a tested metric.